Comparing VPS deals with DDoS protection is more complicated than checking whether a hosting plan includes a security badge. A provider may filter certain network attacks automatically while charging extra for advanced mitigation, application security, or specialized support.
For ecommerce websites, SaaS applications, gaming communities, and business services, the real question is whether visitors can still reach your server during an attack. This guide explains included protection versus paid add-ons and compares OVHcloud, Vultr, Hostwinds, ,以及 GTHost without treating every security feature as equivalent.
What Does DDoS Protection on a VPS Actually Cover?
A distributed denial-of-service attack attempts to exhaust network capacity, server resources, or application processing. Network-layer attacks often target bandwidth or connection handling. Application-layer attacks can resemble legitimate HTTP requests and may require different controls.
Providers commonly describe network mitigation as Layer 3 and Layer 4 protection. It may include traffic analysis, filtering, and scrubbing before malicious packets reach your virtual server. However, protection thresholds, eligible protocols, and response procedures vary.
Never assume that an included feature guarantees uninterrupted service or covers every attack. Read the exact service terms and ask how legitimate traffic is preserved during mitigation.
Included DDoS Protection vs Paid Security Add-ons
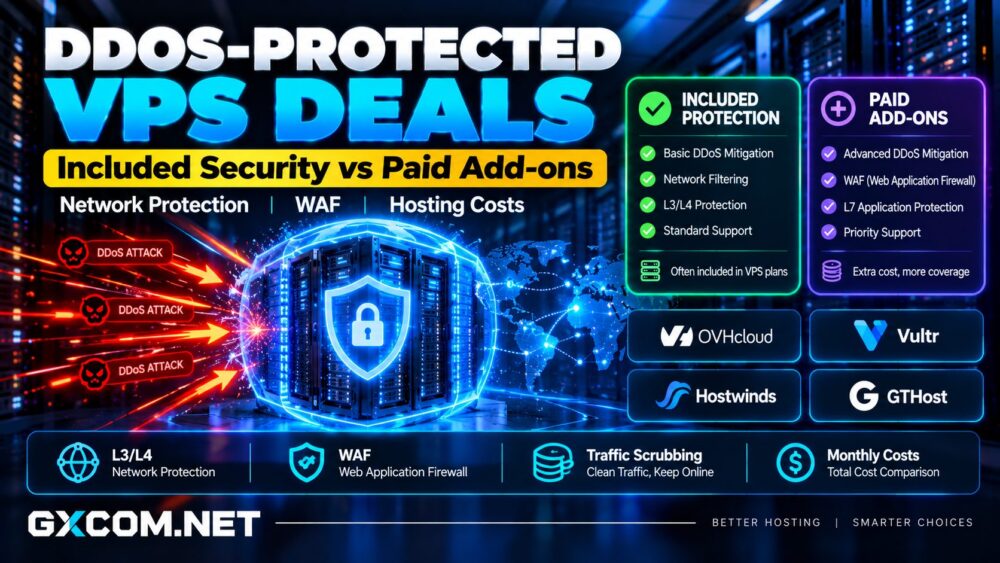
Included protection generally means a defined mitigation capability is bundled with an eligible hosting product. This can reduce the need to purchase a separate network-filtering service, but the scope may be limited.
Paid add-ons can provide additional capabilities such as managed application filtering, web application firewalls, premium traffic scrubbing, specialized routing, or incident assistance. Not every provider offers these services as VPS add-ons.
A CDN or WAF can help protect websites, particularly HTTP-based applications, but it does not automatically protect exposed SSH, game, or custom TCP and UDP services. Match each security layer to the protocols your business uses.
Four VPS Providers Worth Comparing
OVHcloud: Included Network Anti-DDoS
OVHcloud is a relevant starting point for buyers seeking VPS hosting with integrated network anti-DDoS measures. Its infrastructure emphasizes network-level mitigation, although product eligibility and applicable protections should be checked for the selected region and service.
Compare the VPS plan’s CPU, RAM, storage, bandwidth, and backup options alongside its security documentation. Network mitigation should not be confused with a managed WAF or complete application security.

For websites or services exposed directly to the internet, ask what happens when traffic is filtered, whether specific protocols receive different treatment, and what monitoring information customers can access.
Vultr: Cloud Flexibility and Security Planning
Vultr offers cloud compute infrastructure suitable for self-managed applications. DDoS-related options and availability can depend on the product and location, so confirm the current protection terms rather than assuming every instance includes identical mitigation.
Vultr may appeal to teams combining VPS hosting with application firewalls, monitoring, and broader cloud architecture. Developers should account for the operational work required to secure exposed services.
Review instance specifications, bandwidth accounting, and any separate security charges before comparing its total monthly cost with bundled alternatives.
Hostwinds: VPS Hosting with Management Choices
Hostwinds offers VPS hosting with different management arrangements. It is worth evaluating when operational support and security responsibilities influence purchasing decisions.
Check whether DDoS mitigation is included in the exact VPS package or sold separately, and distinguish network filtering from server administration. Managed support does not necessarily include protection against every attack or unlimited incident response.
Ask about firewall configuration, backup restoration, support escalation, and the provider’s policy when a destination receives unusually high attack traffic.
GTHost: Verify Protection by Server Product
GTHost offers server hosting products that may interest customers prioritizing infrastructure control and network characteristics. Buyers should verify that the specific VPS offering and location provide the required DDoS mitigation before ordering.
Request written clarification about filtering capacity, protected protocols, mitigation activation, and possible null routing. A dedicated-server security feature should never be assumed to apply automatically to a VPS product.
For any provider, documented protection terms are more useful than a generic claim of being attack resistant.
Why Blackhole Routing and False Positives Matter
Some networks respond to severe attacks by temporarily discarding traffic to the targeted IP address. This approach, often called blackhole or null routing, can protect shared infrastructure while making the affected service unreachable.
Other mitigation systems may mistakenly block legitimate visitors. Ask whether the provider offers traffic reports, filtering adjustments, escalation procedures, and clear restoration criteria.
For customer-facing applications, measure successful requests and availability during incidents, not merely the volume of malicious packets dropped.
How Much Does DDoS-Protected VPS Hosting Cost?
Calculate the complete monthly expense: VPS rental, security subscriptions, backups, monitoring, additional IP addresses, and any administration services.
For example, a hypothetical $14 VPS with a $9 security add-on and $4 backup service costs $27 monthly. A $23 plan with suitable included protection and backups could be cheaper overall.
These figures illustrate a calculation, not live supplier quotations. The more expensive option may still be preferable if its coverage better matches your actual exposure.
Compare baseline VPS value using our 便宜的VPS服务商指南 and review long-term commitments before choosing a promotion.
Protecting Websites, APIs, and Game Servers
Websites benefit from layered defenses: upstream network mitigation, CDN caching where appropriate, a properly configured WAF, application rate limits, and server monitoring. Origin IP exposure can weaken a proxy-based protection strategy.

APIs need authentication, sensible request limits, and capacity planning. Game servers may depend on UDP or other protocols that a web-focused CDN cannot proxy.
我们的 最佳VPS服务商对比 helps evaluate infrastructure quality, while the 托管型与非托管型主机指南 explains who handles ongoing security work.
Checklist Before Buying a Protected VPS
Ask whether mitigation is automatic, which layers and protocols are covered, whether traffic is rate-limited or null-routed, and how incidents are reported. Confirm the service’s acceptable-use policy and whether repeated attacks can trigger suspension.
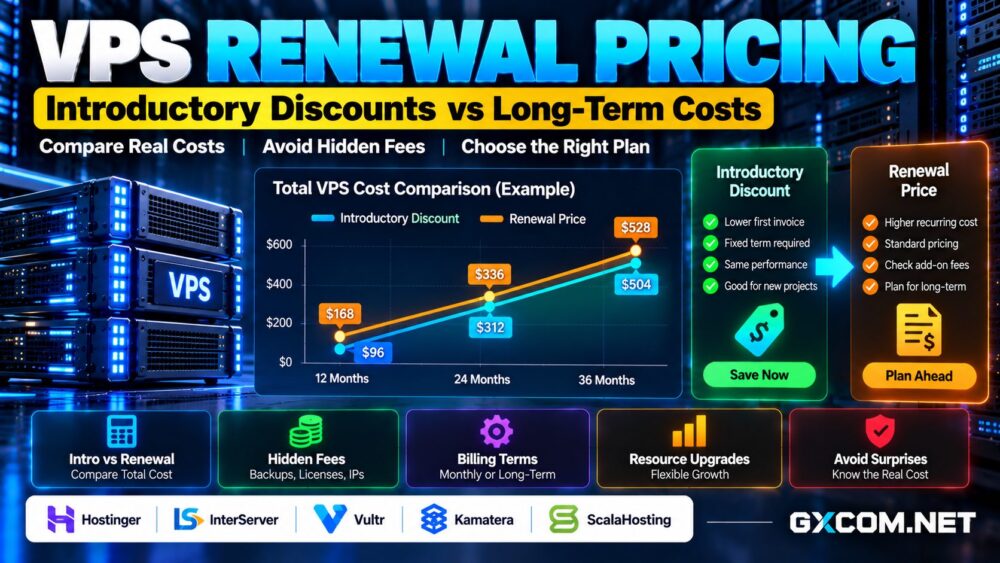
Then examine renewal pricing, included traffic, data-center location, recovery access, and backup retention. Test ordinary latency and application behavior before moving a production workload.
For related purchasing decisions, see our US VPS location and bandwidth comparison 以及 Linux VPS root access guide.
Final Verdict: Buy Coverage, Not a Security Label
OVHcloud deserves attention for integrated network mitigation. Vultr provides cloud flexibility, Hostwinds offers management choices, and GTHost merits investigation when the exact product’s protection terms meet your requirements.
最好的 DDoS-protected VPS deal combines documented mitigation, acceptable service continuity, realistic administration responsibilities, and predictable total costs. Compare written coverage and operational outcomes before paying for security add-ons.