A Rust server can have a powerful processor, sufficient RAM, and fast NVMe storage yet still become unreachable when its network connection is overwhelmed. For public PvP communities, unexpected disconnections during raids, wipes, or major events can quickly damage player confidence.
这就是为什么 Rust server DDoS protection should be a core hosting requirement rather than an optional feature. Effective protection depends on network capacity, traffic filtering, attack detection, routing, and the provider’s ability to respond when an incident occurs.
This guide explains how DDoS attacks affect Rust hosting, which security features matter most, and how to evaluate a protected hosting plan without relying on exaggerated marketing claims.
Why Rust Servers Need DDoS Protection
Rust is a persistent multiplayer survival game where players invest considerable time gathering resources, constructing bases, and defending territory. Public servers may attract highly competitive communities, making service availability particularly important.
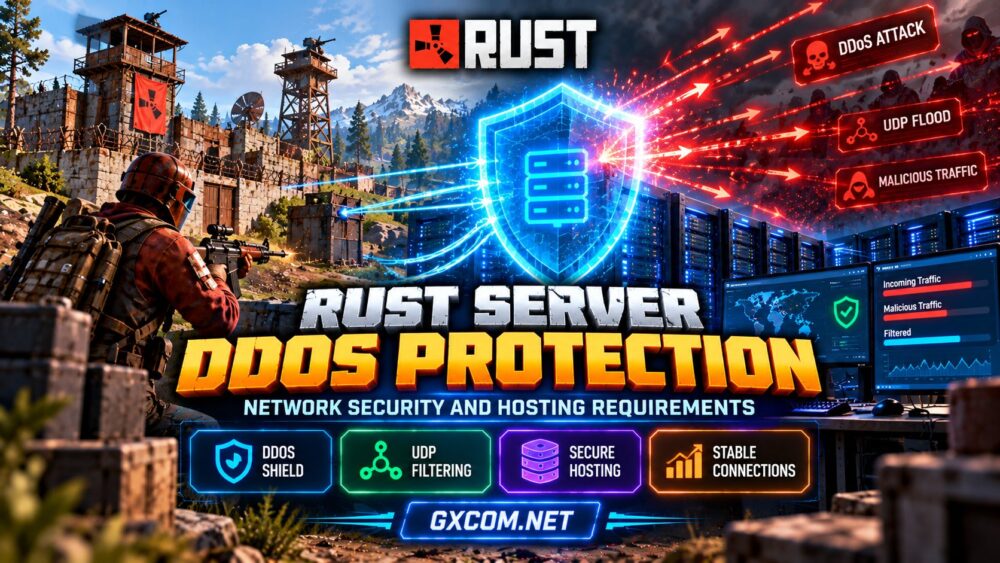
A distributed denial-of-service attack attempts to disrupt a service by overwhelming network or system resources with traffic from multiple sources. A successful attack may prevent legitimate players from connecting even when the game server itself is functioning normally.
Common symptoms include widespread timeouts, sudden disconnections, unusually high packet loss, and an unreachable server address. However, these symptoms do not prove an attack occurred.
Before concluding that DDoS traffic is responsible, administrators should also investigate normal performance bottlenecks using our Rust 服务器延迟与性能指南.
How DDoS Attacks Affect Rust Server Networks
Rust game traffic relies heavily on UDP communication. UDP is useful for time-sensitive multiplayer networking, but hosting infrastructure must distinguish legitimate gameplay traffic from unwanted or excessive packets.
Attacks can target different parts of the service:
- Volumetric attacks: Attempt to saturate available network bandwidth.
- Protocol-level attacks: Exploit network or transport-layer resource limitations.
- Service-targeted floods: Generate disruptive traffic toward the game server’s exposed network services.
These categories can overlap. The appropriate mitigation depends on the traffic pattern, provider infrastructure, and how accurately filtering systems recognize legitimate Rust connections.
Importantly, a standard web application firewall is not a substitute for protection designed to handle game-server traffic.
Essential Rust Server DDoS Protection Features
1. Network-Level Traffic Filtering
Protection should operate before malicious traffic exhausts the server’s network connection. Upstream filtering can reduce unwanted traffic before it reaches the hosting node.
Ask whether the provider includes mitigation for the actual game-server IP and UDP ports, rather than protecting only its website or control panel.
2. UDP-Aware Mitigation
Rust servers need filtering that can accommodate legitimate UDP gameplay. Overly aggressive rules may block valid connections, while ineffective rules can allow disruptive traffic through.
Providers should be able to explain, at an appropriate level, whether their mitigation is designed for game traffic and how legitimate sessions are handled during an incident.
3. Sufficient Upstream Capacity
Local firewall rules cannot solve every attack. If an upstream connection is saturated, legitimate traffic may never reach the server.
Network capacity and upstream mitigation arrangements therefore matter. However, a large advertised mitigation figure does not automatically guarantee effective protection against every attack type.
4. Attack Detection and Response
Automated detection can help identify abnormal traffic patterns, but administrators also need a clear support process when service becomes unavailable.

Check whether the provider documents incident reporting, escalation procedures, and customer communication during major network disruptions.
5. Network Visibility
Useful monitoring may include traffic graphs, packet-loss observations, connection errors, and incident notifications.
Customers do not necessarily need access to raw mitigation infrastructure, but enough information should be available to distinguish network incidents from ordinary server lag.
Network DDoS Protection vs Server Firewall Security
DDoS mitigation and firewall configuration solve related but different problems. A firewall can restrict access to unnecessary services, while upstream mitigation is intended to address disruptive traffic before it overwhelms connectivity.
| 安全层 | 主要目的 | 重要限制 |
|---|---|---|
| Upstream DDoS mitigation | Filter disruptive traffic before delivery | Effectiveness depends on attack characteristics |
| Network firewall | Control permitted ports and connections | Cannot recover an already saturated upstream link |
| Operating-system firewall | Restrict host-level network access | Consumes local resources and depends on reachable connectivity |
| 账户安全 | Protect administrative access | Does not stop network flooding |
| 备份 | Support recovery from data loss | Do not prevent network outages |
A secure hosting arrangement combines these controls instead of treating one feature as complete protection.
For additional server-hardening considerations, review our 游戏服务器安全检查清单.
How Server Location Affects DDoS Protection
Server location influences latency, routing, and access to network mitigation infrastructure. A nearby data center may offer low normal ping, but the quality of its upstream connectivity still matters.
During mitigation, traffic may be filtered or rerouted through specialized infrastructure. Depending on the network design, this can change latency or routing behavior.
When comparing regions, ask whether protection is included at the selected location and whether the same policies apply across different facilities.
我们的 Rust server hosting locations guide explains how to evaluate geographic placement and player latency.
Managed Rust Hosting vs VPS and Dedicated Servers
Managed game hosting can simplify routine deployment, game updates, and control-panel administration. It may also include network protection, depending on the provider and selected plan.
A self-managed VPS offers greater operating-system control, but the customer typically remains responsible for firewall configuration, software maintenance, and many troubleshooting tasks.
Dedicated servers provide additional resource control and isolation. Nevertheless, dedicated hardware alone does not provide DDoS protection.
For administrators evaluating infrastructure options, our Gaming VPS vs Dedicated Server comparison 解释了其中的权衡。.
值得比较的 Rust 托管服务商
Host Havoc and 生存服务器 are two established game-hosting names to investigate when comparing Rust hosting options. Review the currently offered plans, locations, support policies, and published network-protection terms.
GameServerKings is another candidate for administrators comparing managed Rust server packages. Confirm which security features apply to the exact service you intend to purchase.
Godlike.Host 以及 Sparked 主持人 can also be included in a broader game-hosting shortlist, subject to current Rust product availability and regional coverage.
These names are comparison candidates, not a verified ranking of mitigation effectiveness. Published security specifications and direct provider confirmation should determine whether a particular plan meets your requirements.
Rust DDoS Protection: Hosting Requirements Checklist
| 要求 | 应提出的问题 |
|---|---|
| UDP protection | Is mitigation designed for Rust game traffic? |
| Protected IP | Does protection cover the actual server address? |
| Regional coverage | Is the selected data center included? |
| Mitigation policy | Are there exclusions or traffic-related restrictions? |
| 事件响应 | How are major outages escalated? |
| 网络监控 | Can administrators review relevant incident information? |
| 恢复计划 | Are backups and restoration procedures available? |
Request clarification before ordering whenever the product page uses broad claims such as “advanced protection” without explaining coverage or limitations.
What to Do When Your Rust Server Is Under Attack
If your server suddenly becomes unreachable, begin with a controlled incident-response process rather than making several configuration changes simultaneously.
- Confirm the symptoms: Check server availability, player reports, and monitoring information.
- Rule out ordinary failures: Review recent updates, crashes, resource usage, and provider status notices.
- Contact the hosting provider: Report the affected service, approximate start time, and observed connectivity problems.
- Preserve useful evidence: Keep relevant logs and monitoring screenshots without exposing sensitive account information.
- Follow the provider’s instructions: Avoid uncoordinated changes that could interfere with mitigation or investigation.
- Communicate with players: Share confirmed service updates without publishing unnecessary infrastructure details.
After connectivity returns, review the incident and identify whether monitoring, support arrangements, or hosting protections should be improved.

Common Mistakes When Choosing Protected Rust Hosting
- Assuming every plan from a provider includes identical DDoS protection.
- Comparing only advertised mitigation capacity without examining UDP compatibility.
- Ignoring the network policies of the selected server location.
- Believing that a powerful CPU or additional RAM can prevent network saturation.
- Failing to establish a support escalation process before an outage.
- Confusing DDoS mitigation with backups or administrative account security.
常见问题解答
Does every Rust server need DDoS protection?
Public Rust servers should strongly consider it because network availability directly affects gameplay. The appropriate protection level depends on exposure, community size, and operational requirements.
Can a firewall alone stop a DDoS attack?
Not always. Local filtering cannot restore connectivity when unwanted traffic has already saturated the upstream network connection.
Does DDoS protection increase Rust server ping?
It can affect routing or latency depending on the mitigation design and whether traffic is being redirected. There is no universal latency penalty that applies to every provider.
Is dedicated Rust hosting automatically more secure?
No. Dedicated hardware provides resource isolation, but network mitigation, software maintenance, firewall policies, and access controls must still be evaluated separately.
最终裁决
生效 Rust server DDoS protection requires more than a security badge on a hosting product page. Administrators should prioritize UDP-aware mitigation, upstream filtering, regional coverage, clear support procedures, and reliable monitoring.
When evaluating Host Havoc, Survival Servers, GameServerKings, Godlike.Host, or Sparked Host, compare the documented protection attached to each specific Rust hosting plan. A well-matched network and a clear incident-response process can be more valuable than impressive but unexplained security claims.
For broader purchasing research, see our 最佳 Rust 服务器托管对比.